Category: Government IT
-
Palo Alto Networks has released critical updates to fix a zero-day vulnerability (CVE-2024-3400) in its firewall operating system PAN-OS. The flaw allows unauthenticated attackers to gain root access through command injection in the GlobalProtect gateway/portal. Hotfixes are available, and customers are advised to apply mitigation measures. The U.S. CISA has also mandated actions to address…
-
The XZ Compression Backdoor Timeline details a supply chain attack on the xz compression library by “Jia Tan,” who gained trust and eventually inserted a backdoor, affecting systems using the library. The attack was detected in March 2024, prompting industry response and highlighting vulnerabilities in open source supply chain security.
-

Online retailer PandaBuy was compromised, exposing 1.3 million customers’ data, prompting users to change passwords and enable two-factor authentication. Similarly, a ransomware attack affected over 2.8 million individuals through Massachusetts Health Insurer, triggering lawsuits and the offer of credit monitoring.
-

Sam Bankman-Fried, founder of the defunct cryptocurrency exchange FTX, has been sentenced to 25 years in prison for extensive financial misconduct. The case highlights the urgency of enhanced Anti-Money Laundering (AML) and Countering Financing of Terrorism (CFT) measures in the cryptocurrency sector. The industry must strengthen AML/CFT protocols and collaboration with regulators to ensure market…
-
The Cybersecurity and Infrastructure Security Agency (CISA) has updated its Known Exploited Vulnerabilities Catalog to include CVE-2023-24955, a high-severity Remote Code Execution (RCE) vulnerability in Microsoft SharePoint Server. This vulnerability, coupled with CVE-2023-29357, poses a significant threat, demanding immediate mitigation efforts to prevent potential cyberattacks. CISA urges all organizations to prioritize remediation.
-
PCI DSS is crucial for businesses handling credit card info. Common mistakes include neglecting security assessments, storing data incorrectly, weak passwords, lack of employee training, non-compliant third-party vendors, and more. To ensure compliance, businesses can consult cybersecurity experts and utilize Netizen’s services for built-in security and compliance support.
-
Microsoft Corp. is set to unveil artificial intelligence tools on April 1, aimed at enhancing the capabilities of cybersecurity professionals. These tools, developed in partnership with OpenAI, will assist in summarizing suspicious incidents and uncovering hackers’ methods. Dubbed Copilot for Security, this suite of AI tools was unveiled approximately a year ago and has since…
-
Over the last half-decade, TikTok has swiftly climbed to a leading position within the realm of social media, captivating a worldwide audience with its short, intriguing video content. Owned by the Chinese technological behemoth ByteDance, TikTok has been the focus of intense international scrutiny and debate, mainly from Western governments. The heart of this debate…
-
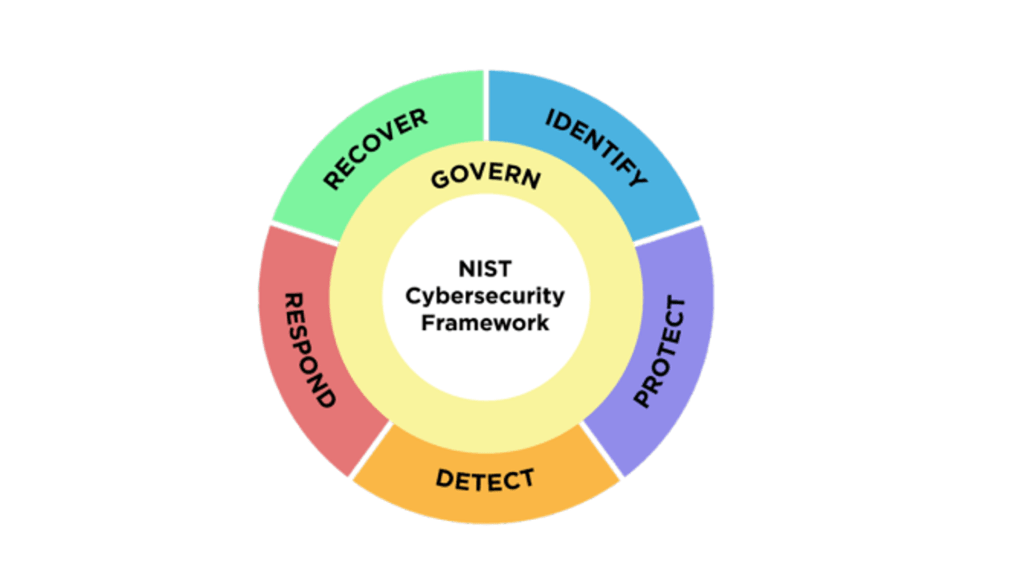
The National Institute of Standards and Technology (NIST) has officially released version 2.0 of its landmark Cybersecurity Framework (CSF), marking its first major update since the framework’s inception in 2014. The revised framework introduces significant enhancements designed to extend its applicability and effectiveness across a broader spectrum of organizations, ranging from the smallest schools and…
-
Overview: Phish Tale of the Week After the Takedown: LockBit Ransomware’s Resurgence Alarming Surge in BlackCat Ransomware Targets U.S. Healthcare How can Netizen help? Phish Tale of the Week Often times phishing/smishing campaigns, created by malicious actors, target users by utilizing social engineering. For example, in this text message, the actors are appearing as Coinbase…

