Category: Technology
-
British cybersecurity firm Sophos has faced ongoing attacks from state-sponsored Chinese hackers since 2018. These attackers exploit vulnerabilities and adapt tactics, targeting critical sectors. Sophos’ proactive measures include deploying software implants for real-time monitoring. Collaborating with international agencies, the firm emphasizes the need for innovative defense strategies against increasingly sophisticated threats.
-

SynthID, developed by Google DeepMind, embeds invisible watermarks in AI-generated content to verify authenticity, enhancing cybersecurity and combatting disinformation. Though resilient, its effectiveness is limited to Google’s models, and it raises new privacy and security concerns. Open-sourcing SynthID may foster broader applications in digital content verification.
-
Fortinet has revealed a serious vulnerability in its FortiManager API, identified as CVE-2024-47575, which enables attackers to access sensitive information, including configuration files and credentials. Despite warnings issued to customers, early exploitation was reported before the disclosure, leading to frustration over Fortinet’s delayed notification and transparency regarding this critical flaw.
-
In February 2023, Lehigh Valley Health Network experienced a significant cyberattack by the BlackCat ransomware group, exposing sensitive patient data. The incident raised concerns about cybersecurity readiness and trust. Despite efficient emergency responses, LVHN faced lawsuits leading to a $65 million settlement, highlighting the need for enhanced defenses in healthcare against cyber threats.
-

In October 2024, Microsoft addressed 118 vulnerabilities, including five zero-days, two actively exploited. Key vulnerabilities included three critical remote code executions. Other patched vulnerabilities ranged from elevation of privilege to denial of service. Users are urged to apply these patches promptly, while Adobe also released key updates for its products.
-
PTaaS combines automated and human assessments to enhance an organization’s cyber posture. It enables continuous testing, offers real-time reporting and strategic recommendations, and includes comprehensive coverage, continuous scanning, customizable testing, and dedicated expertise. PTaaS provides ongoing security management, constant access to security experts, reduced costs, industry standard adherence, swifter turnaround, real-time testing, and more control.…
-
GreyNoise Intelligence has identified “Noise Storms,” involving spoofed web traffic from millions of IPs, suggesting potential links to Chinese state-sponsored actors. These sophisticated attacks manipulate traffic through TTL spoofing and targeted tactics. Despite ongoing investigations, the precise motivations remain unclear, prompting calls for enhanced cybersecurity measures and global collaboration in monitoring these anomalies.
-
Insider threats pose a significant risk to organizations, involving misuse of legitimate access. The Netizen Insider Threat Kill Chain offers a structured approach, highlighting key phases and strategies for effective management. To address common security gaps, a comprehensive approach integrating behavioral analytics, user activity monitoring, and data loss prevention is crucial. Netizen provides advanced solutions,…
-
Network security is crucial for organizational strength, requiring a multi-layered approach to tackle evolving cyber threats. Cloud security demands comprehensive strategies, while IDPS and digital forensics employ advanced technologies to evolve alongside threats. Companies like Netizen offer advanced solutions, including CISO-as-a-Service and compliance support, to protect critical IT infrastructure and ensure regulatory compliance.
-
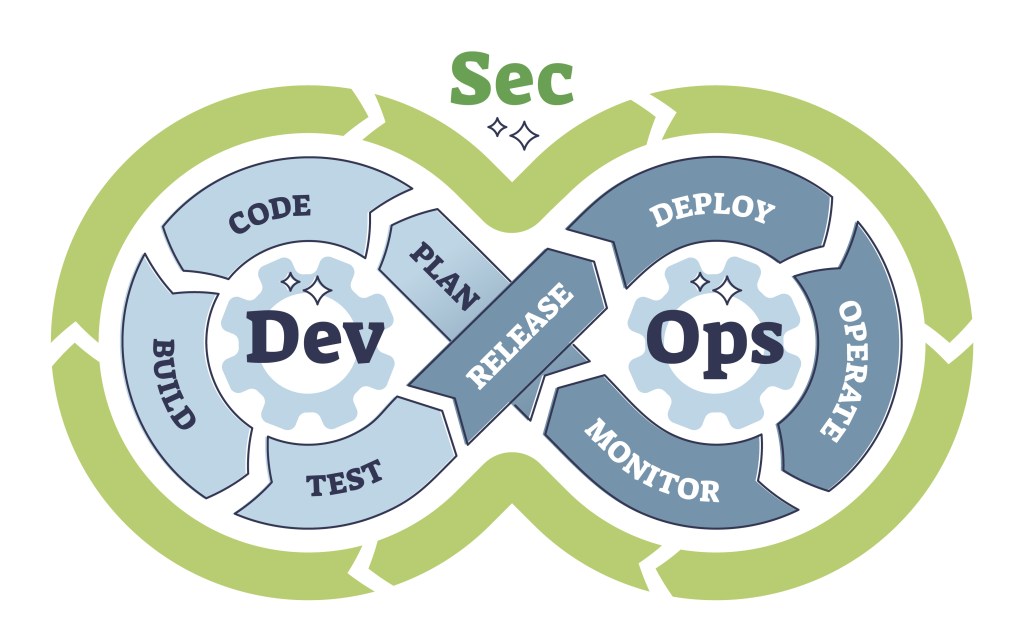
DevOps, DevSecOps, and security posture are essential in modern software development, but often misunderstood. DevOps integrates development and operations to speed up deployment. DevSecOps adds security early in the Agile process and into the containerization and orchestration with automation and thorough documentation. Effective collaboration and cultural change are vital for DevSecOps success.

