Category: Technology
-
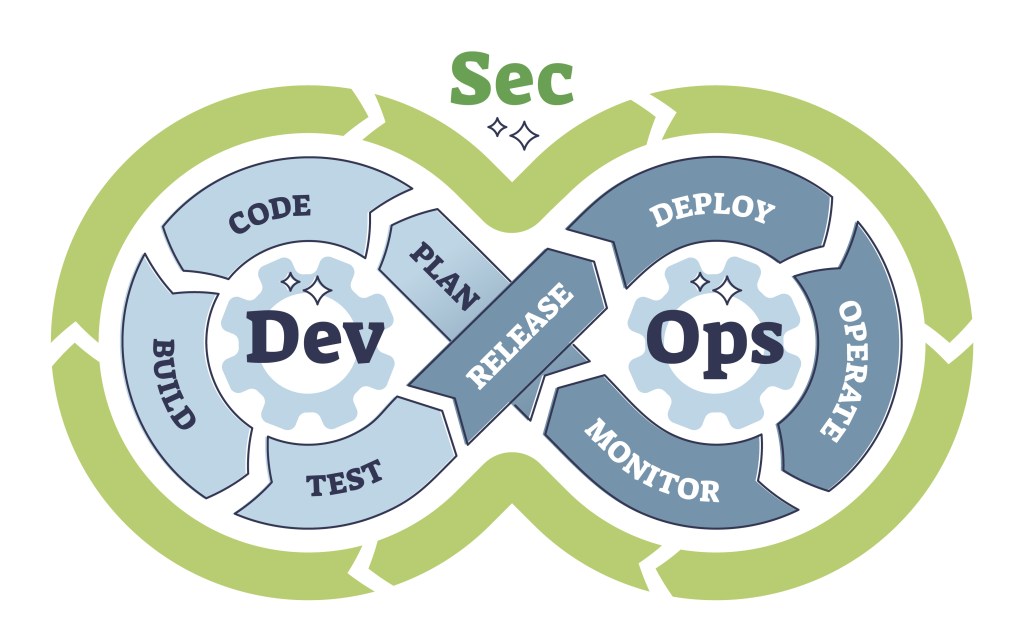
DevOps, DevSecOps, and security posture are essential in modern software development, but often misunderstood. DevOps integrates development and operations to speed up deployment. DevSecOps adds security early in the Agile process and into the containerization and orchestration with automation and thorough documentation. Effective collaboration and cultural change are vital for DevSecOps success.
-
When evaluating ISO 27001 and ISO 27002, it’s essential to understand their distinct roles and purposes in the realm of information security management. Although both standards are closely related, they serve different functions, and recognizing these differences can help you implement them more effectively. General Differences ISO 27001 and ISO 27002 have distinct objectives, which…
-
Volt Typhoon, a Chinese state-sponsored hacking group, has emerged as a significant player in global cybersecurity, focusing particularly on critical infrastructure. This detailed analysis explores Volt Typhoon’s operations, the impacts of its activities, and how we can effectively defend against such threats. Understanding these aspects is crucial for protecting national security and maintaining global stability.…
-
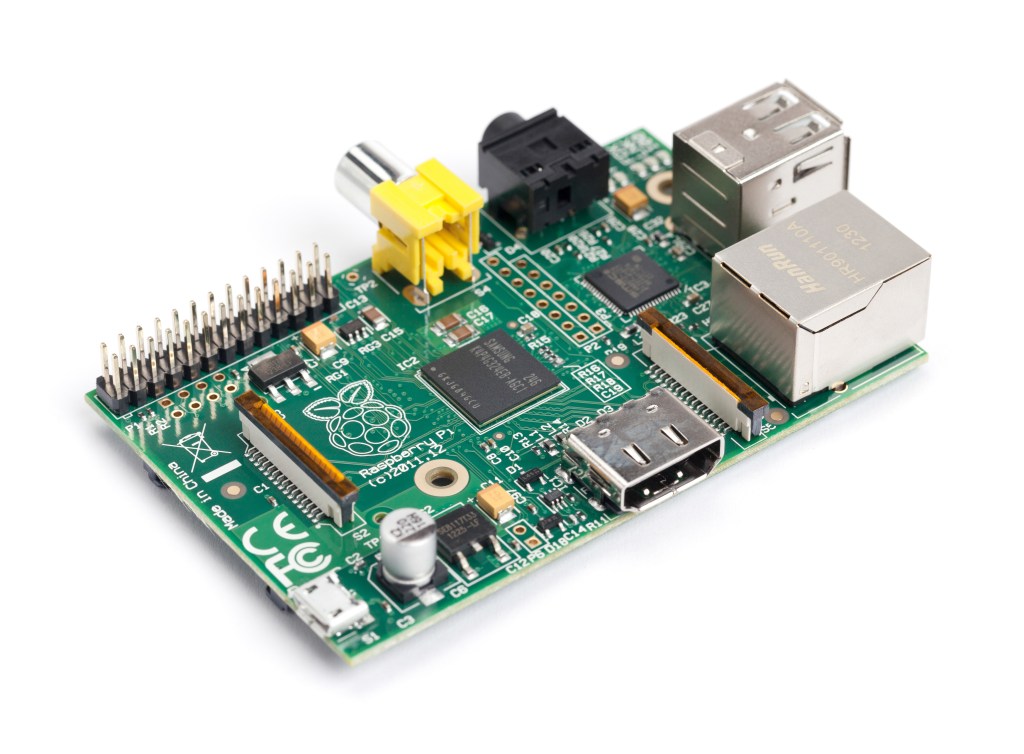
Penetration testing is a flexible skill for cybersecurity analysts. A drop box, like the one built with a Raspberry Pi 3 and TP-Link AC1300 Wi-Fi adapter, provides secure, cost-effective, and easy network access. Netizen offers cybersecurity services, including penetration testing, vulnerability assessments, and automation tools. Visit www.netizen.net/contact for inquiries.
-
DDoS attacks are a significant threat to internet security that disrupt normal traffic by overwhelming servers. Identifying and mitigating DDoS attacks is crucial. Detection involves monitoring traffic patterns, analyzing sources, and using Intrusion Detection Systems. Mitigation strategies include blackhole routing, rate limiting, Web Application Firewall, and Anycast network diffusion. Netizen offers advanced security solutions and…
-

The cybersecurity industry continues to experience rapid growth, driven by the increasing frequency and sophistication of cyber threats. For those looking to start a career in this field, there are numerous entry-level opportunities that offer a solid foundation and promising career trajectory. This guide provides an overview of some common entry-level cybersecurity roles, highlighting key…
-

Firewalls are essential for data protection. Next Generation Firewalls (NGFWs) go beyond traditional firewalls, offering advanced features like application control, intrusion prevention, and cloud-delivered threat intelligence. NGFWs provide comprehensive security, addressing modern cyber threats effectively. While traditional firewalls have their place, NGFWs are superior for robust network protection in today’s digital landscape.
-

Large language models like GPT-4 raise concerns as they can autonomously exploit cybersecurity vulnerabilities, posing a significant threat. These AI advancements may enhance defense measures but also empower malicious actors. The cybersecurity community must proactively develop defensive measures and regulate the deployment of these models to mitigate potential risks.
-
KnowBe4, a cybersecurity firm, faced a security breach involving a North Korean hacker posing as an employee. Although no data was compromised, the incident prompted tighter hiring and vetting processes. Organizations can prevent insider threats by implementing end-user training, UEBA tools, MFA, network segmentation, monitoring, incident response, and clear policies. Netizen offers advanced cybersecurity solutions…
-
The Policy Enforcement Point (PEP) is a crucial part of the Attribute-Based Access Control (ABAC) architecture, ensuring consistent access control and security for enterprise data. It intercepts user requests, evaluates attributes, and communicates with the Policy Decision Point (PDP) to determine access, providing robust security for modern applications.
 Netizen Blog and News
