Category: Technology
-
A single file moved between NIPRNet and SIPRNet can become a classification, authorization, malware, information-flow, and audit event at the same time. For Department of Defense organizations, moving information between the Non-classified Internet Protocol Router Network and the Secret Internet Protocol Router Network is fundamentally different from transferring a file between ordinary enterprise networks. The…
-

A new U.S. government warning has put one of industrial automation’s most widely deployed controller families at the center of an active cyber campaign. The concern is not limited to vulnerable software sitting somewhere inside a plant network. The targeted devices can directly control pumps, valves, motors, production lines, safety processes, and other equipment whose…
-
Encryption can remain operational long after it stops being a sound security decision, leaving organizations with cryptographic dependencies that become harder, more expensive, and more dangerous to replace each year. Across enterprise infrastructure, government networks, operational technology, identity systems, embedded devices, and long-lived applications, cryptography has accumulated over decades of deployment. Algorithms have changed. Protocols…
-
The security question around artificial intelligence is shifting from what a model can generate to what an agent can reach, invoke, change, and carry forward. For much of the early generative AI security discussion, risk was framed around outputs: hallucinated information, data leakage, jailbreaks, unsafe code, or a user convincing a model to ignore an…
-

“Need to know” is often treated as a procedural phrase associated with classified environments, regulated data, or sensitive internal operations. In security architecture, the principle has a much broader technical meaning. It describes an authorization model in which access is granted based on a demonstrable operational requirement, rather than merely on identity, job title, network…
-
Microsoft’s August 2026 Patch Tuesday addresses 400 vulnerabilities, including one actively exploited zero-day and two publicly disclosed zero-days. The release contains 42 critical vulnerabilities, with 37 classified as remote code execution flaws and five as elevation of privilege issues. Although the total falls below July’s record 570 vulnerabilities, August remains an unusually large Patch Tuesday…
-

A missing tenant boundary in the back end of AI meeting assistant tl;dv reportedly allowed any authenticated user to enumerate meeting records belonging to other customers, including live calls hosted by government agencies, universities, and major companies. The issue did not require a stolen administrator account, malware, or a flaw in Google Cloud itself. According…
-
Ransomware detection used to look like a malware identification task. A security product inspected a file, compared its code or hash against known indicators, and blocked it when the artifact matched a known family. That model still has value, but it is no longer sufficient for many modern intrusions. Human-operated ransomware can arrive through legitimate…
-
Cloud forensics often begins too late. A security team detects suspicious activity, opens an incident, and starts asking which logs exist, how long they have been retained, who can access them, and whether a compromised administrator could delete them. Responders discover that object-level access logging was never enabled, identity records expired weeks earlier, a container…
-
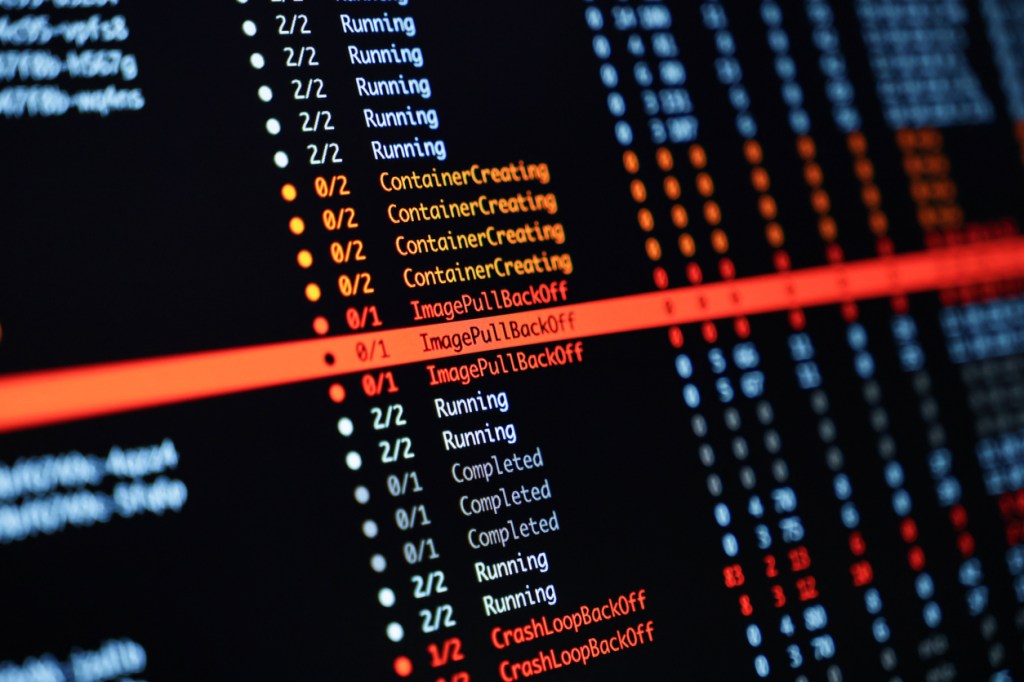
Kubernetes is built to make communication between workloads simple. Pods receive routable IP addresses, Services provide stable endpoints, and internal DNS allows applications to locate one another without tracking where each container is running. Those features make distributed systems easier to operate, but they can also produce a broad internal attack surface when network controls…

