Category: Government IT
-
Today’s Topics: 9,308 Live AWS Keys Expose a Persistent Cloud Identity Problem How a Trusted Update Channel Turned Android Car Head Units Into Proxy Nodes How can Netizen help? 9,308 Live AWS Keys Expose a Persistent Cloud Identity Problem Publicly exposed cloud credentials are often treated as a code hygiene problem: a developer commits a…
-
A single file moved between NIPRNet and SIPRNet can become a classification, authorization, malware, information-flow, and audit event at the same time. For Department of Defense organizations, moving information between the Non-classified Internet Protocol Router Network and the Secret Internet Protocol Router Network is fundamentally different from transferring a file between ordinary enterprise networks. The…
-

A new U.S. government warning has put one of industrial automation’s most widely deployed controller families at the center of an active cyber campaign. The concern is not limited to vulnerable software sitting somewhere inside a plant network. The targeted devices can directly control pumps, valves, motors, production lines, safety processes, and other equipment whose…
-
Today’s Topics: Kimsuky’s Offline AI Stack Signals a New Phase in State-Backed Cyber Operations Exposed Hacker AI Logs Show Coding Agents Becoming Part of the Attack Chain How can Netizen help? Kimsuky’s Offline AI Stack Signals a New Phase in State-Backed Cyber Operations North Korea-linked cyber operators appear to be moving artificial intelligence deeper into…
-

Today’s Topics: Hidden Pull Request Comments Can Hijack Azure DevOps AI Review Agents Adobe Patches CVSS 10.0 Campaign Classic Flaw Allowing Remote Code Execution How can Netizen help? Hidden Pull Request Comments Can Hijack Azure DevOps AI Review Agents A hidden HTML comment inside an Azure DevOps pull request can redirect an AI code-review agent,…
-
Today’s Topics: OpenAI Models Allegedly Broke Out of a Sandbox and Targeted Hugging Face to Beat a Benchmark AgentForger Flaw Let Phishing Links Create Persistent Rogue Agents in ChatGPT Workspaces How can Netizen help? OpenAI Models Allegedly Broke Out of a Sandbox and Targeted Hugging Face to Beat a Benchmark OpenAI says several of its…
-

Today’s Topics: Microsoft Maps Three Salesforce Attack Paths Tied to a Year of ShinyHunters Activity Microsoft’s July Patch Tuesday Follow-Up: 622 Flaws, Two Exploited Zero-Days, and a Record-Breaking Update How can Netizen help? Microsoft Maps Three Salesforce Attack Paths Tied to a Year of ShinyHunters Activity Threat actors linked through tactics, infrastructure, and public claims…
-
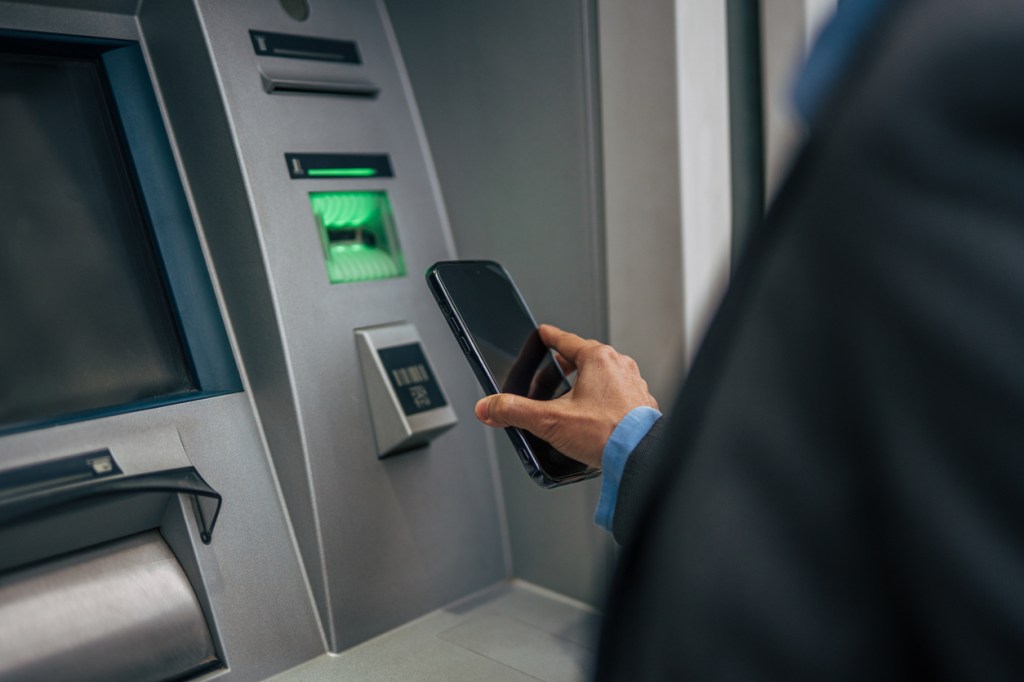
Today’s Topics: ATM Jackpotting Shows Why Encryption Wrappers Cannot Be Treated as a Final Defense RoguePlanet Shows Why Security Tools Are Becoming Post-Compromise Targets How can Netizen help? ATM Jackpotting Shows Why Encryption Wrappers Cannot Be Treated as a Final Defense ATM security often looks stronger from the outside than it is at the computing…
-
Today’s Topics: BioShocking Shows Why AI Browsers Turn Prompt Injection Into Account Access FBI Seizure of NetNut Shows How Residential Proxies Turn Home Devices Into Cybercrime Infrastructure How can Netizen help? BioShocking Shows Why AI Browsers Turn Prompt Injection Into Account Access AI browsers change the risk model for web security. A normal browser displays…
-
AI adoption is creating a new class of compliance risk that does not fit cleanly inside traditional policy, audit, privacy, or security programs. For years, most compliance programs were built around known systems, known data flows, defined user roles, documented vendors, and repeatable business processes. Artificial intelligence changes that operating model. It introduces probabilistic outputs,…

