Category: Threat Intelligence
-
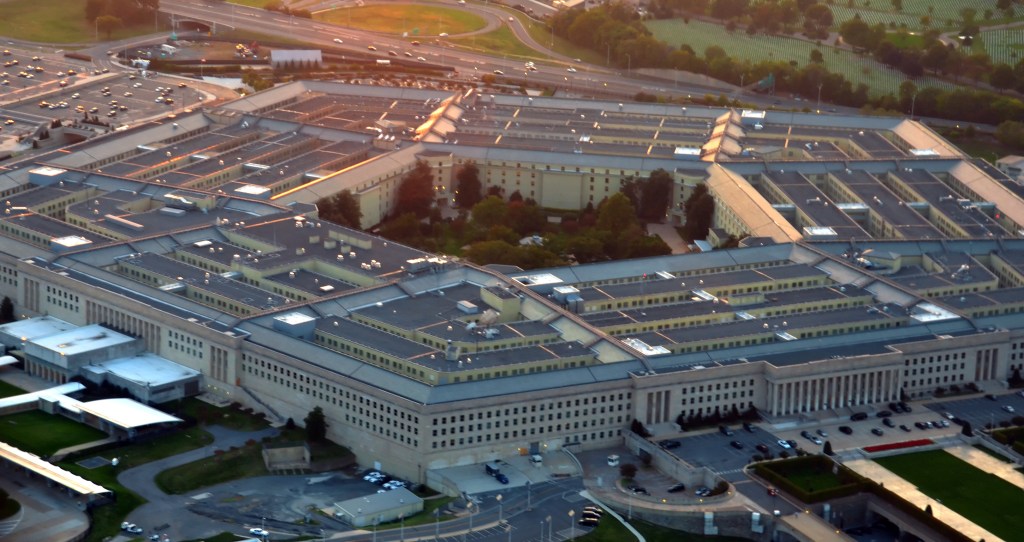
In a significant shift, OpenAI, the creator of ChatGPT, has announced collaboration with the Pentagon on various software projects, including those related to cybersecurity. This announcement marks a substantial departure from the organization’s prior stance, as it had previously imposed a ban on employing its artificial intelligence technology for military purposes. Military Engagement and Ethical…
-
SMTP smuggling, a novel cybersecurity threat, has emerged as a significant concern due to its ability to exploit vulnerabilities in the Simple Mail Transfer Protocol (SMTP). This protocol is widely used by mail servers for the transmission, reception, and relaying of emails. Discovered by Timo Longin from SEC Consult, SMTP smuggling allows malicious actors to…
-

The year 2023 marked a significant surge in phishing attacks targeting cryptocurrency wallets, highlighting the increasing sophistication of cybercriminal activities in the blockchain space. These attacks, impacting a wide range of networks including Ethereum, Binance Smart Chain, Polygon, Avalanche, and nearly 20 others, have led to substantial financial losses, totaling nearly $295 million stolen from…
-
Security vulnerabilities are a constant threat to business operations, making prompt patching crucial. Netizen’s Security Operations Center highlights five critical vulnerabilities from December, emphasizing the need for immediate action. These include issues with Microsoft Power Platform Connector, Google Chrome’s WebRTC framework, Apache Struts, SSH ProxyCommand, and Apache OFBiz. Netizen offers comprehensive security solutions and support.
-
Overview: Phish Tale of the Week The Cyberattack on Ukraine’s Largest Mobile Network: Kyivstar Teen Members of LAPSUS$ Gang Sentenced in UK for Hacking Spree How can Netizen help? Phish Tale of the Week Often times phishing campaigns, created by malicious actors, target users by utilizing social engineering. For example, in this text message, the…
-
In a significant cybersecurity development, ESET, a leading Slovak cybersecurity firm, has unearthed a deceptive network of 18 malicious loan apps, collectively known as “SpyLoan.” These apps, designed to exploit users seeking financial services, have been downloaded over 12 million times. Primarily targeting regions in Southeast Asia, Africa, and Latin America, SpyLoan apps masquerade as…
-
AI training data poisoning is a form of cybersecurity threat that targets the integrity of machine learning models by deliberately inserting misleading or harmful data into the training set. This tactic can compromise the model’s accuracy, leading to incorrect or manipulated outputs. Nightshade, a tool developed by Ben Zhao’s team at the University of Chicago,…
-

Two significant vulnerabilities have been identified in the WebKit web browser engine, impacting a range of Apple devices and operating systems. These vulnerabilities are critical and require immediate attention. CVE-2023-42916: This is an out-of-bounds read issue in WebKit. It presents a risk of leaking sensitive information when processing web content. Such a vulnerability can be…
-

Functioning as a Telegram bot-based toolkit, Telekopye, an e-commerce threat vector, streamlines the execution of advanced phishing operations. It enables perpetrators, referred to as ‘Neanderthals’, to deploy a range of tactics including spear-phishing through crafted HTML pages, domain spoofing, and social engineering via SMS and email phishing campaigns. This toolkit marks a significant escalation in…
-
Security vulnerabilities are a constant threat to businesses. Netizen’s Security Operations Center has identified five critical vulnerabilities from November that require immediate attention. These include privilege escalation, path traversal, SQL injection, CSRF, and local privilege escalation issues in various software. Netizen offers advanced solutions and services to help businesses enhance their cybersecurity posture.

