Category: Threat Intelligence
-
Containers are supposed to make workloads easier to isolate, deploy, and manage, but the infrastructure controlling those containers can create a far more direct path into the host. One of the clearest examples is the Docker Remote API, which gives administrators and automation systems programmatic control over the Docker daemon. If that interface is exposed…
-
Files have always been a security boundary. Applications have spent decades defending against malicious documents, path traversal, parser flaws, archive bombs, embedded scripts, unsafe deserialization, and executable content disguised as ordinary attachments. AI agents do not replace those risks. They introduce a new one by allowing the contents of a file to influence what the…
-
Enterprise AI rarely operates inside a single application boundary. A user may submit a prompt through one interface, an orchestration layer may add system instructions, a retrieval service may query internal documents, an embedding model may convert those documents into vectors, and a separate model provider may process the assembled context. From there, observability tools…
-
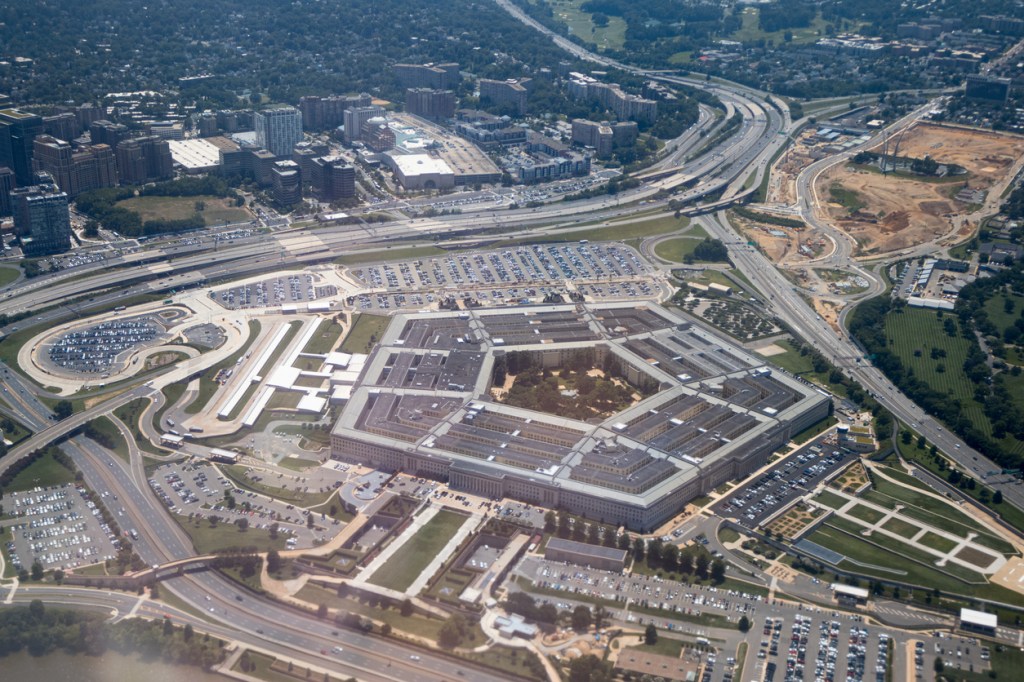
Today’s Topics: Google Pauses Open-Source Bug Bounty Submissions Amid AI Report Flood Pentagon Personnel Breach Exposes Data on Nearly Three Million People How can Netizen help? Google Pauses Open-Source Bug Bounty Submissions Amid AI Report Flood Google has spent years encouraging security researchers to automate more of the work involved in finding software flaws. Now,…
-
Microsoft released its 2026 Digital Defense Report on October 1, offering a broad look at how cyber threats have changed as artificial intelligence becomes integrated into both attacker workflows and enterprise systems. The report paints a security environment moving faster and becoming more interconnected, but one where many of the underlying weaknesses remain familiar. Attackers…
-
Metadata is easy to dismiss as background information. A document has an author, creation date, file path, revision history, and perhaps a few tags. A photograph may contain location data and device information. A cloud instance has an identifier, region, role, and networking details. A Kubernetes object carries labels and annotations that help administrators organize…
-
Today’s Topics: Google’s €403 Million Fine Shows the Cost of Losing Control of Location Data CMMC Phase II Is Paused, but Defense Contractors Still Have Work to Do How can Netizen help? Google’s €403 Million Fine Shows the Cost of Losing Control of Location Data On September 21, Ireland’s Data Protection Commission fined Google €403…
-
The FBI is investigating claims that the ShinyHunters cybercrime group compromised FBIJobs.gov and obtained a large collection of personnel and applicant information, including records that appear to identify employees working in sensitive intelligence, surveillance, and counterintelligence roles. ShinyHunters says it entered through a previously unknown Oracle PeopleSoft vulnerability and ultimately stole between two and three…
-
Today’s Topics: ScreenConnect Flaw Turns a Trusted Remote Session Into a File Execution Path Cisco ISE Zero-Day Turns an Identity Control Point Into Root Access How can Netizen help? ScreenConnect Flaw Turns a Trusted Remote Session Into a File Execution Path Remote support software already occupies an unusually trusted position inside an enterprise. A technician…
-
A Software Bill of Materials can answer one of the hardest questions in software security: what is actually inside this product? That answer has real operational value. When a new vulnerability appears in a widely used library, an SBOM can help an organization determine which applications contain the affected component without manually inspecting every product.…

