Category: Open Source
-
With 70% of Microsoft’s 850 million active users on Windows 10, IT teams face critical transitions as the End of Support deadline approaches. Microsoft’s aggressive push for Windows 11 brings challenges like hardware upgrades and user resistance. Proactive planning and strategy are vital for seamless migration and operational security during this change.
-

In October 2024, Microsoft addressed 118 vulnerabilities, including five zero-days, two actively exploited. Key vulnerabilities included three critical remote code executions. Other patched vulnerabilities ranged from elevation of privilege to denial of service. Users are urged to apply these patches promptly, while Adobe also released key updates for its products.
-
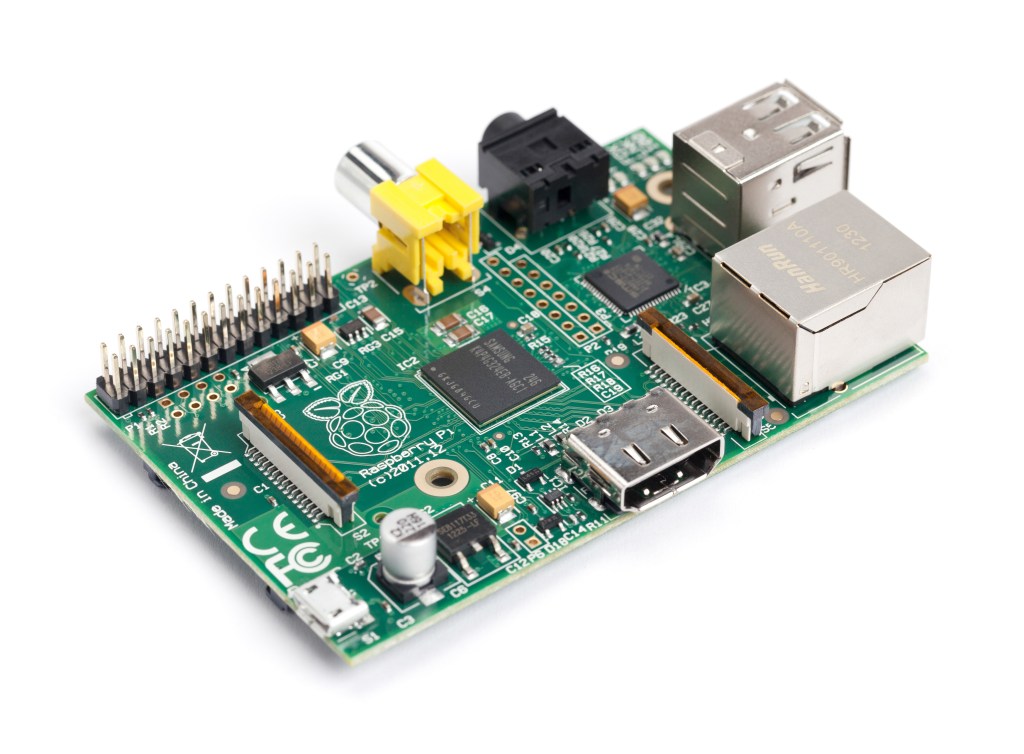
Penetration testing is a flexible skill for cybersecurity analysts. A drop box, like the one built with a Raspberry Pi 3 and TP-Link AC1300 Wi-Fi adapter, provides secure, cost-effective, and easy network access. Netizen offers cybersecurity services, including penetration testing, vulnerability assessments, and automation tools. Visit www.netizen.net/contact for inquiries.
-
Switzerland has enacted EMBAG, mandating open-source software use in the public sector, promoting transparency and security. The US has a cautious approach due to security concerns, but may need to reassess. Open source fosters innovation, cost savings, and enhances security.
-
Cryptography has been crucial in securing data since ancient times, evolving from the Caesar cipher to modern blockchain technology. Blockchain heavily relies on cryptography to ensure data integrity and security. Public and private keys, digital signatures, hashing, and cryptographic algorithms like SHA-256 and ECDSA play vital roles in blockchain security. Common vulnerabilities, recent advancements, and…
-

SIEM, or Security Information and Event Management, is a crucial tool that helps organizations detect and respond to security threats effectively. Over the years, SIEM has evolved to include advanced features like AI-driven automation, compliance management, and real-time threat recognition, making it an indispensable part of modern cybersecurity. At Netizen, we understand the importance of…
-
The XZ Compression Backdoor Timeline details a supply chain attack on the xz compression library by “Jia Tan,” who gained trust and eventually inserted a backdoor, affecting systems using the library. The attack was detected in March 2024, prompting industry response and highlighting vulnerabilities in open source supply chain security.
-
Microsoft Corp. is set to unveil artificial intelligence tools on April 1, aimed at enhancing the capabilities of cybersecurity professionals. These tools, developed in partnership with OpenAI, will assist in summarizing suspicious incidents and uncovering hackers’ methods. Dubbed Copilot for Security, this suite of AI tools was unveiled approximately a year ago and has since…
-
Web 3.0, often referred to as the Semantic or Decentralized Web, has emerged over the past few years as a both an ideological and technological shift from the current state of the internet, referred to as Web 2.0. The new technology is defined by decentralized databases and distributed ledgers across nodes, reducing the risks in…
-
A critical vulnerability within the GNU C Library (glibc) has recently come to light, putting a spotlight on the inherent complexities and potential oversights in system security, even within well-established, widely used open-source software. This vulnerability granted the name “Looney Tunables” by the researchers from Qualys, resides in glibc’s dynamic loader, a crucial component in…

