Category: Government
-

Data disposal, a critical component of information lifecycle management, involves the processes and methods used to permanently remove or delete data from digital storage devices. This practice is essential in managing data securely, ensuring that once data is no longer required, it cannot be recovered or misused. Data disposal works by overwriting the original data…
-
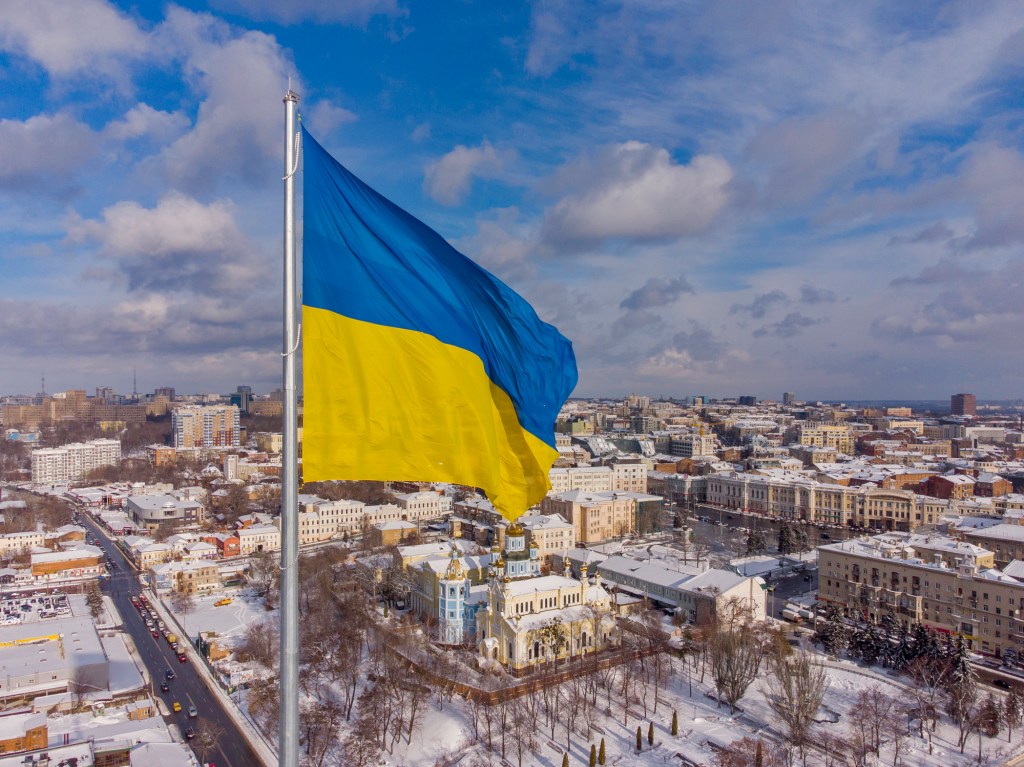
Ukraine has found itself at the center of a sophisticated cyber-attack campaign, where over 2,000 computers have been compromised by the malware strain known as DirtyMoe. This malicious software, active since 2016, is notorious for its capabilities in executing cryptojacking and distributed denial-of-service (DDoS) attacks. The Computer Emergency Response Team of Ukraine (CERT-UA) attributes these…
-
Overview: Phish Tale of the Week Microsoft’s Response to the Midnight Blizzard Cyberattack Environmental Services Industry Faces Unprecedented DDoS Attacks How can Netizen help? Phish Tale of the Week Often times phishing campaigns, created by malicious actors, target users by utilizing social engineering. For example, in this text message, the actors are appearing as Netflix…
-

On Thursday, the Office of Foreign Assets Control (OFAC) under the U.S. Department of the Treasury announced sanctions against the North Korean-affiliated group Kimsuky, along with eight international agents accused of aiding in evading sanctions. These sanctions, imposed against the North Korean cyberespionage group, (which is also known as APT43) mark a significant step in…
-

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has taken a significant step towards enhancing the cybersecurity posture of the nation’s critical infrastructure sectors. The agency has announced the launch of an innovative pilot program, aimed at extending cutting-edge cybersecurity shared services to critical infrastructure entities, especially those most in need of such support. This…
-
The FBI recently released a PIN (Private Industry Notification) in order to “highlight emerging ransomware trends,” in this case “dual ransomware attacks,” a type of attack that targets the same organization twice with two different types of ransomware, resulting in a significantly more encrypted system for the victims. A dual ransomware attack is classified by…
-

The list of export-restricted military documents leaked by players of the popular free-to-play game War Thunder just got longer. The flight manual for the F-117 Nighthawk, a stealth aircraft manufactured by Lockheed Martin, was posted on the War Thunder official site forum, a place for community discussion about various War Thunder related topics like in-game…
-
Overview: Phish Tale of the Week North Korean Hackers Could be About to Cash Out 41 Million in Stolen Bitcoin New WinRAR Zero-Day Vulnerability Could Install Malware When You Unzip Files How can Netizen help? Phish Tale of the Week Phishing attempts can often target specific groups that can be exploited by malicious actors and…
-
Overview Phish Tale of the Week Hackers target United Nations in latest data breach U.S SEC changes stance on Cybersecurity. What does this mean for your business? How can Netizen help? Phish Tale of the Week Phishing attempts can often target specific groups that can be exploited by malicious actors. In this instance, we see…
-
Overview Phish Tale of the Week Colonial Pipeline Didn’t have MFA in Place, Neither Do Most Defense Contractors US Defense Contractors Fail to Meet CMMC Requirements How can Netizen help? Phish Tale of the Week Phishing attempts can often target specific groups that can be exploited by malicious actors. In this instance, we see a…

