Category: CyberSecurity
-
As we delve deeper into 2024, ransomware continues to morph, presenting new challenges for cybersecurity professionals worldwide. This evolving landscape requires constant vigilance and adaptation of defense strategies. Here, we explore the most significant trends in ransomware evolution and how they’re shaping the cyber threat horizon. Double Extortion and Beyond Ransomware attacks are increasingly incorporating…
-
Recently, the healthcare sector faced a significant cybersecurity challenge when Change Healthcare, a prominent healthcare payment and management solutions provider, became the target of a sophisticated cyberattack by ransomware group BlackCat. This blog post offers an in-depth analysis of the incident, exploring the specifics of the breach, identifying the perpetrators, and assessing its profound impact…
-
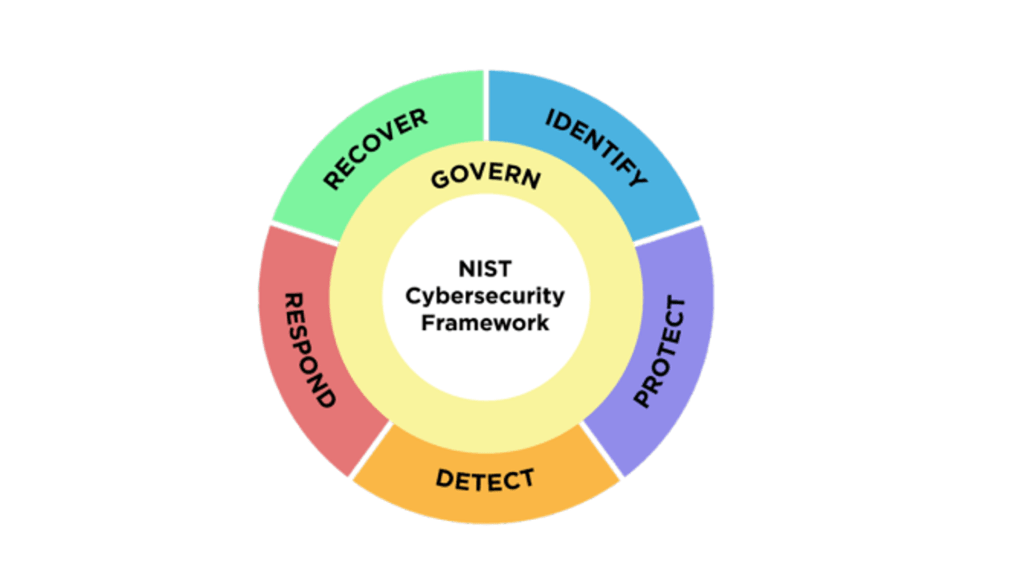
The National Institute of Standards and Technology (NIST) has officially released version 2.0 of its landmark Cybersecurity Framework (CSF), marking its first major update since the framework’s inception in 2014. The revised framework introduces significant enhancements designed to extend its applicability and effectiveness across a broader spectrum of organizations, ranging from the smallest schools and…
-
Overview: Phish Tale of the Week After the Takedown: LockBit Ransomware’s Resurgence Alarming Surge in BlackCat Ransomware Targets U.S. Healthcare How can Netizen help? Phish Tale of the Week Often times phishing/smishing campaigns, created by malicious actors, target users by utilizing social engineering. For example, in this text message, the actors are appearing as Coinbase…
-

Security vulnerabilities are a common occurrence in managing any business’s organizational security. The prompt patching and remediation of any new vulnerabilities are critical to reducing the outside attack surface. Netizen’s Security Operations Center (SOC) has compiled five vulnerabilities from February that should be immediately patched or addressed if present in your environment. Detailed writeups below:…
-
Microsoft has unveiled PyRIT (Python Risk Identification Tool), a pioneering open-access framework designed to enhance the security of generative AI technologies. This innovative tool aims to support the proactive identification of potential risks within AI systems, focusing on both security threats and responsible AI considerations, such as fairness and the accuracy of generated content. PyRIT…
-
The UK’s National Crime Agency (NCA) successfully thwarted LockBit, a notorious global cybercrime syndicate known for ransomware attacks. The operation, named Cronos, involved seizing control of LockBit’s network and was a collaborative effort with international law enforcement. This highlights the evolving capabilities of law enforcement against cyber threats and emphasizes the commitment to supporting recovery…
-

Data disposal, a critical component of information lifecycle management, involves the processes and methods used to permanently remove or delete data from digital storage devices. This practice is essential in managing data securely, ensuring that once data is no longer required, it cannot be recovered or misused. Data disposal works by overwriting the original data…
-
Fortinet has recently issued a warning about two critical-severity vulnerabilities within its FortiSIEM platform. These vulnerabilities, identified as CVE-2024-23108 and CVE-2024-23109, both received the highest level of concern with a provisional Common Vulnerability Scoring System (CVSS) score of 10. These vulnerabilities have a high potential to be exploited without any form of authentication, a prospect…
-
In a recent SEC filing, Clorox, the American manufacturing giant known for its consumer and professional cleaning products, has disclosed the financial aftermath of a cyberattack that struck the company in August 2023. This cyber incident, which commenced on August 11, led to the company identifying unauthorized activities within its systems, prompting immediate action to…

