Category: Business Solutions
-
Hackers are increasingly targeting supply chains, exploiting vulnerabilities in third-party systems to breach larger networks. Recent high-profile attacks leveraged flaws in common IT tools, causing significant disruptions. To mitigate risks, organizations must implement advanced supplier risk management, secure software pipelines, keep systems updated, and strengthen access controls, among other strategies.
-
Insider threats pose a significant risk to organizations, involving misuse of legitimate access. The Netizen Insider Threat Kill Chain offers a structured approach, highlighting key phases and strategies for effective management. To address common security gaps, a comprehensive approach integrating behavioral analytics, user activity monitoring, and data loss prevention is crucial. Netizen provides advanced solutions,…
-
Penetration testing, also known as ethical hacking, is essential for evaluating cybersecurity defenses. To prepare effectively for a test, define technical objectives and scope, assemble a response team, obtain authorization, and prepare the environment. Communicate technical details, define reporting and remediation processes, and conduct post-test activities to strengthen security posture. Netizen offers comprehensive cybersecurity services,…
-
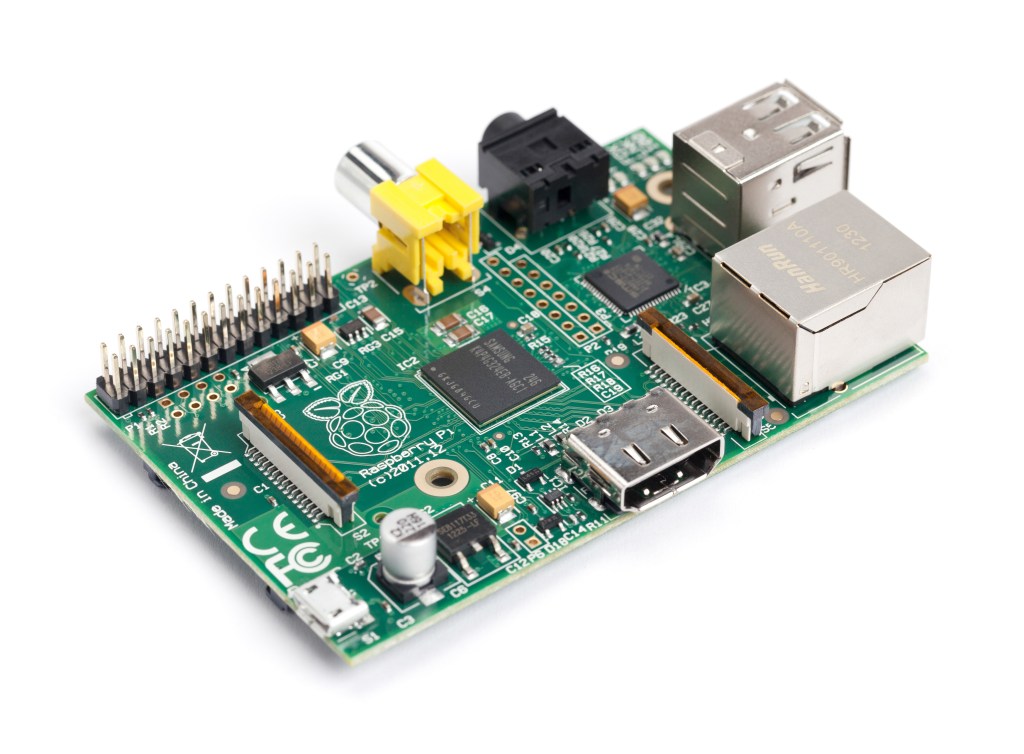
Penetration testing is a flexible skill for cybersecurity analysts. A drop box, like the one built with a Raspberry Pi 3 and TP-Link AC1300 Wi-Fi adapter, provides secure, cost-effective, and easy network access. Netizen offers cybersecurity services, including penetration testing, vulnerability assessments, and automation tools. Visit www.netizen.net/contact for inquiries.
-
A federal court ruled that a company can be held liable for a data breach at its law firm, permitting a negligence claim against Mondelez Global LLC. This underscores the importance of thorough third-party risk management and data security measures, including evaluations, data minimization, contractual safeguards, continuous monitoring, and robust incident response.
-
Identity and Access Management (IAM) is crucial for controlling access to sensitive information, ensuring security, compliance, and efficiency. It centralizes user identities and access rights, streamlining their management and enforcing precise access controls. IAM verifies user identities, manages access, supports productivity, reduces data breach risks, and simplifies compliance with regulations.
-

In today’s tech-driven business landscape, cybersecurity is paramount. A Virtual Chief Information Security Officer (vCISO) plays a crucial role in managing and enhancing an organization’s cybersecurity program, offering expertise without the need for a full-time, on-site CISO. Their cost-effectiveness and flexibility make them vital for businesses of all sizes, especially in the face of growing…
-

SIEM, or Security Information and Event Management, is a crucial tool that helps organizations detect and respond to security threats effectively. Over the years, SIEM has evolved to include advanced features like AI-driven automation, compliance management, and real-time threat recognition, making it an indispensable part of modern cybersecurity. At Netizen, we understand the importance of…
-
The evolving cyberthreat landscape poses a significant risk to small and medium-sized businesses (SMBs), with reported breaches increasing by 57% and exposed records up by 29%. To safeguard against these threats, SMBs should implement critical cybersecurity practices, including SSL certificate management, multi-factor authentication, firewalls, regular data backups, incident response planning, and more.
-
In the intricate landscape of modern business, adhering to regulatory compliance standards is not just an obligation; it’s a critical component of sustainable operation. The challenge, however, lies in the relentless evolution of these regulations and the complexity of ensuring consistent compliance across all facets of an organization. To effectively manage this complexity and uphold…

