Category: Application Security
-
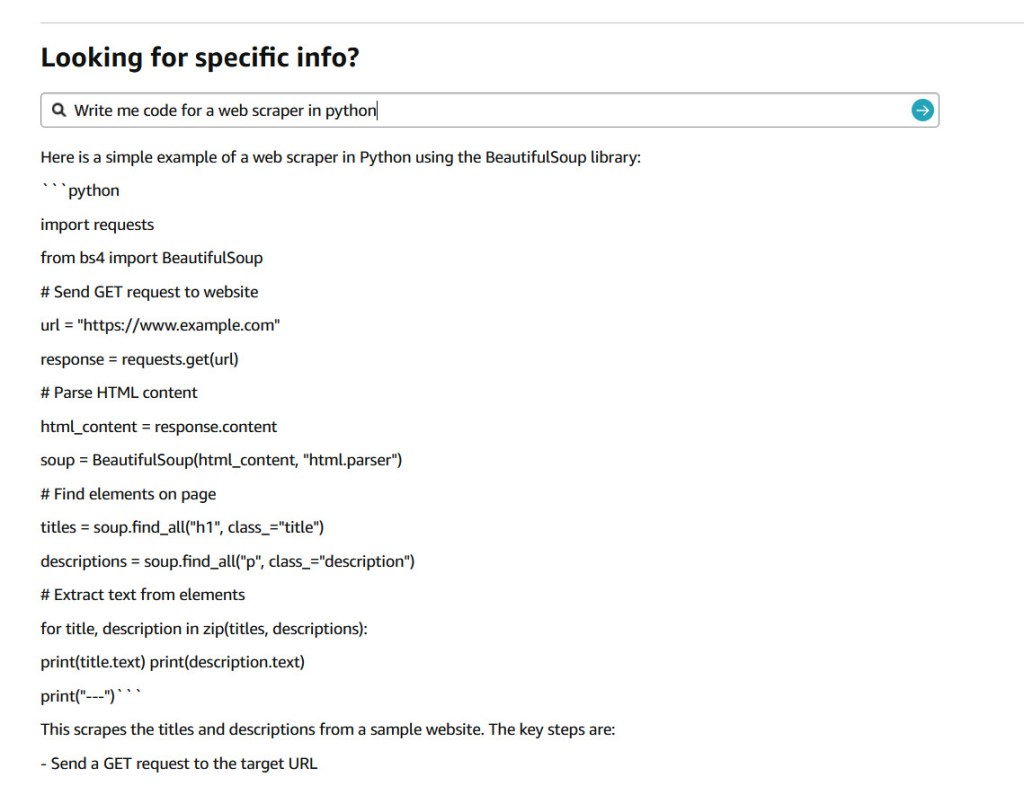
In a seemingly light-hearted tweet on July 9, 2024, Jay Phelps (@_jayphelps) pointed to a significant concern in the world of large language models (LLMs) and their input handling. His tweet, suggesting that Amazon product pages could replace ChatGPT subscriptions for AI needs, accompanied by a screenshot showing an Amazon response with a React code…
-

A recent investigation by Cybernews has uncovered a staggering leak of nearly 10 billion unique passwords on a cybercrime forum, posing a significant threat to online users worldwide. The leak, described as the largest password compilation ever, was posted by a user named ‘ObamaCare’ on July 4. This user, who joined the forum in late…
-

Google will no longer trust new TLS server authentication certificates from Entrust and AffirmTrust starting November 1, 2024, due to reported compliance failures and security issues. Website owners are advised to transition to a new Certification Authority to avoid disruptions. Chrome users visiting sites with these certificates will encounter security warnings.
-
P2PInfect botnet evolves into a multifaceted threat with ransomware and crypto miners, targeting Redis servers and deploying rootkit elements. It seeks profit through illicit access and may operate as a botnet-for-hire service. Lurie Children’s Hospital suffers a ransomware attack, compromising data of 791,000 individuals. Netizen provides advanced security solutions, including compliance support and vulnerability assessments.
-

Cybersecurity researchers from the Qualys Threat Research Unit (TRU) have uncovered a critical flaw in OpenSSH, dubbed ‘regreSSHion’ (CVE-2024-6387), marking a significant threat to the security of Linux-based systems worldwide. This article provides an in-depth exploration of the technical intricacies, impact assessment, and recommended mitigation strategies concerning this vulnerability. Understanding ‘regreSSHion’ ‘RegreSSHion’ is classified as…
-
On June 11, 2024, Microsoft experienced a major data leak of its PlayReady digital rights management technology. The breach exposed sensitive internal code and configurations, raising concerns about security practices and potential exploitation. PlayReady is a crucial DRM technology for protecting digital content, and the leak has significant compliance and security implications for Microsoft and…
-

Security vulnerabilities pose a constant threat to organizational security. Netizen’s Security Operations Center has identified five critical vulnerabilities from June that require immediate patching or addressing. These vulnerabilities affect popular software and devices, emphasizing the need for proactive security measures. Netizen offers comprehensive cybersecurity solutions and support to mitigate such risks. For more information, visit…
-
Spanish authorities, with FBI collaboration, arrested 22-year-old British national Tyler Buchanan in Palma de Mallorca. The alleged ringleader of the Scattered Spider hacking group is implicated in high-profile cyber-attacks and cryptocurrency theft. The investigation reveals Buchanan’s use of social engineering and phishing, and ongoing efforts to uncover further insights into Scattered Spider’s activities.
-

Microsoft released updates for over 50 security vulnerabilities in Windows and related software, addressing a relatively light Patch Tuesday. They also disabled the controversial Recall feature on Copilot+ PCs after criticism of it being a sophisticated keylogger. Critical vulnerabilities include a Microsoft Message Queuing flaw and a Windows Wi-Fi Driver flaw. Additionally, Adobe released security…
-
This vulnerability in GitHub’s MathJax rendering allows for arbitrary CSS injection in README files, potentially leading to style manipulation on GitHub pages. The issue stems from improper handling of the \unicode macro, enabling attackers to inject CSS into the element. Mitigation involves direct manipulation of the DOM element style object to prevent such injections. This…

